Trusted by 170+ Enterprise Clients

After-Hours Alerts Go Unacknowledged Until Morning

how it works
Your monitoring stack already detects the failure. Outside business hours, the alert goes to a shared inbox or an unwatched dashboard, and nobody acknowledges it until someone logs in the next morning. Over a weekend the wait is considerably longer.
Without a Staffed NOC
2:14 a.m.
The payment service fails. The alert fires into an inbox that nobody is watching.
2:14 a.m.
The payment service fails. The alert fires into an inbox that nobody is watching.
2:14 a.m.
The payment service fails. The alert fires into an inbox that nobody is watching.
The investigation started 7 hours after the failure, and a customer reported it first.
Without a Staffed NOC
2:14 a.m.
The payment service fails. The alert fires into an inbox that nobody is watching.
2:14 a.m.
The payment service fails. The alert fires into an inbox that nobody is watching.
2:14 a.m.
The payment service fails. The alert fires into an inbox that nobody is watching.
The incident is resolved before business hours.
The scenario is illustrative and not taken from a client engagement.
Holograph Pattern

Why Multi-Vendor Security Is Hard to Report On

When firewall, endpoint, email security and testing come from different vendors, each reports in its own console and format. An auditor or a customer’s security team expects one view of risk.
how it works
01

Gaps Between Controls

Controls that each pass their own checks can still leave gaps where they meet, such as unmonitored egress traffic or stale firewall rules.
02

Findings in Different Formats

Scanner exports, pentest PDFs and console screenshots do not combine into one report an auditor can use.
03

Nobody Owns the Whole Picture

Each vendor manages its own scope, and nobody is accountable for security across all of them.

How We Run a Security Engagement

We scope and deliver testing, network security, monitoring and identity work under one contract, with Holograph as your single point of contact.

A Dedicated Project Manager

One Holograph project manager owns the engagement from purchase order to handover, across every workstream.

Findings Ranked by Exploitability

We rank each finding by how exploitable it is and the attack path it opens, alongside its CVSS base score.

Remediation Support

We work through the remediation plan with your engineers, starting with the highest-risk findings first.

A Summary Your Board Can Read

Each report pairs an executive summary for leadership with technical detail your engineers can act on.

Services

Find Exploitable Weaknesses Across Your Attack Surface

Vulnerability Assessment
We configure and tune next-generation firewalls and IPS, including rule-base design and cleanup, segmentation policy and high-availability configuration.
Penetration Testing
We configure and tune next-generation firewalls and IPS, including rule-base design and cleanup, segmentation policy and high-availability configuration.
AI Penetration Testing
We configure and tune next-generation firewalls and IPS, including rule-base design and cleanup, segmentation policy and high-availability configuration.
Red Teaming
We configure and tune next-generation firewalls and IPS, including rule-base design and cleanup, segmentation policy and high-availability configuration.
DoS and DDoS Testing
We configure and tune next-generation firewalls and IPS, including rule-base design and cleanup, segmentation policy and high-availability configuration.
Configuration Audit
We configure and tune next-generation firewalls and IPS, including rule-base design and cleanup, segmentation policy and high-availability configuration.
Email Gateway Audit
We configure and tune next-generation firewalls and IPS, including rule-base design and cleanup, segmentation policy and high-availability configuration.
Security Posture Assessment
We configure and tune next-generation firewalls and IPS, including rule-base design and cleanup, segmentation policy and high-availability configuration.
ISO 27001 and SOC 2 Readiness
We configure and tune next-generation firewalls and IPS, including rule-base design and cleanup, segmentation policy and high-availability configuration.

Harden the Network Edge and Every Endpoint

Firewall and Intrusion Prevention
We configure and tune next-generation firewalls and IPS, including rule-base design and cleanup, segmentation policy and high-availability configuration.
Endpoint Security and Antivirus
We configure and tune next-generation firewalls and IPS, including rule-base design and cleanup, segmentation policy and high-availability configuration.
Data Loss Prevention (DLP)
We configure and tune next-generation firewalls and IPS, including rule-base design and cleanup, segmentation policy and high-availability configuration.
Web Application Firewall (WAF) Tuning
We configure and tune next-generation firewalls and IPS, including rule-base design and cleanup, segmentation policy and high-availability configuration.

Detect and Contain Threats

Security Operations Center (SOC) Monitoring
We monitor alerts and logs from your firewalls, endpoints, servers and cloud accounts, with coverage hours agreed at scoping. Analysts categorize each alert, investigate confirmed activity and escalate it with context and a recommended response.
Dark Web Monitoring
We configure and tune next-generation firewalls and IPS, including rule-base design and cleanup, segmentation policy and high-availability configuration.
Digital Forensics and Incident Response
We configure and tune next-generation firewalls and IPS, including rule-base design and cleanup, segmentation policy and high-availability configuration.
Virtual CISO
We configure and tune next-generation firewalls and IPS, including rule-base design and cleanup, segmentation policy and high-availability configuration.
Phishing Simulation and Awareness Training
We configure and tune next-generation firewalls and IPS, including rule-base design and cleanup, segmentation policy and high-availability configuration.

Control Who Has Access to What

Identity and Access Management (IAM)
We configure and tune next-generation firewalls and IPS, including rule-base design and cleanup, segmentation policy and high-availability configuration.
Identity Governance and Administration (IGA)
We configure and tune next-generation firewalls and IPS, including rule-base design and cleanup, segmentation policy and high-availability configuration.
Privileged Access Management (PAM)
We configure and tune next-generation firewalls and IPS, including rule-base design and cleanup, segmentation policy and high-availability configuration.
Identity AI
We configure and tune next-generation firewalls and IPS, including rule-base design and cleanup, segmentation policy and high-availability configuration.
AI Governance
We configure and tune next-generation firewalls and IPS, including rule-base design and cleanup, segmentation policy and high-availability configuration.

Why Multi-Vendor Security Is Hard to Report On

how it works
01

Scope

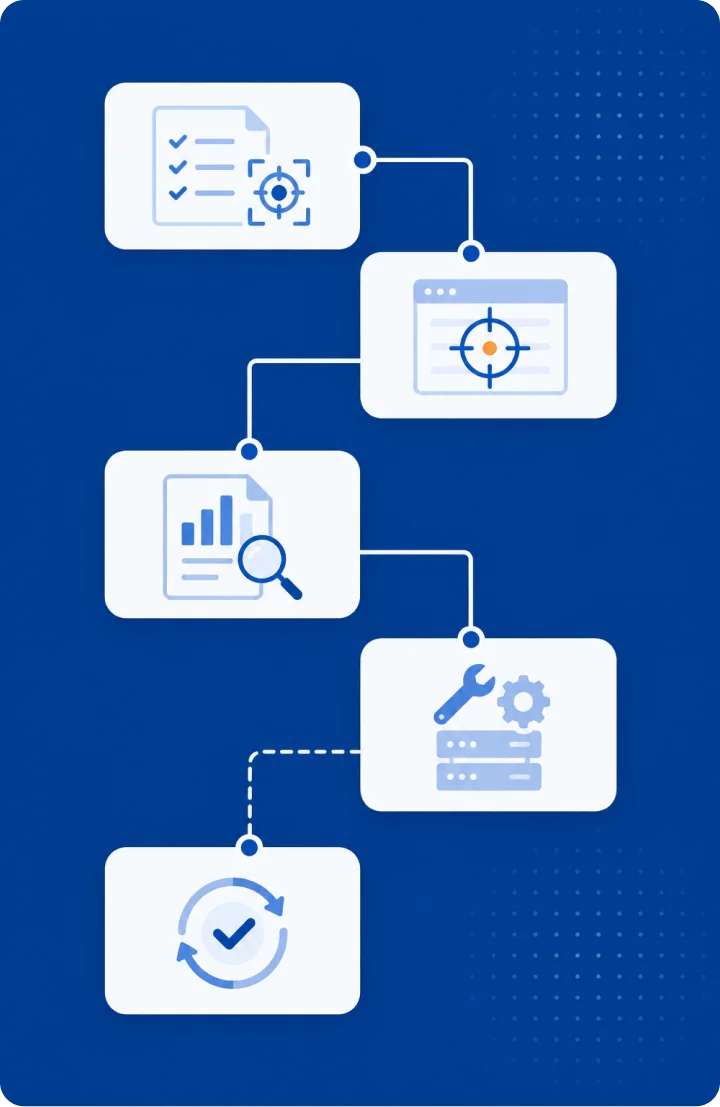
We agree in writing the targets, exclusions, testing windows, test accounts and rules of engagement.
02

Test

Testers work only inside that scope. We escalate critical findings as soon as we confirm them.
03

Report

We deliver evidence, reproduction steps, a risk rating and remediation guidance for each finding.
04

Remediate

Your team applies the fixes, with our support.
05

Retest, Where Agreed

We retest remediated findings when retesting is part of the agreed scope.

What Each Test or Assessment Delivers

Every test and assessment ends with a written report containing:
how it works
An executive summary of risk for leadership
Each finding with evidence, reproduction steps and a severity rating
Remediation guidance specific to your environment
A remediation plan ordered by exploitability
Ask for a Sample Report

Related Services

Frequently Asked Questions

What happens when a failure occurs outside office hours?
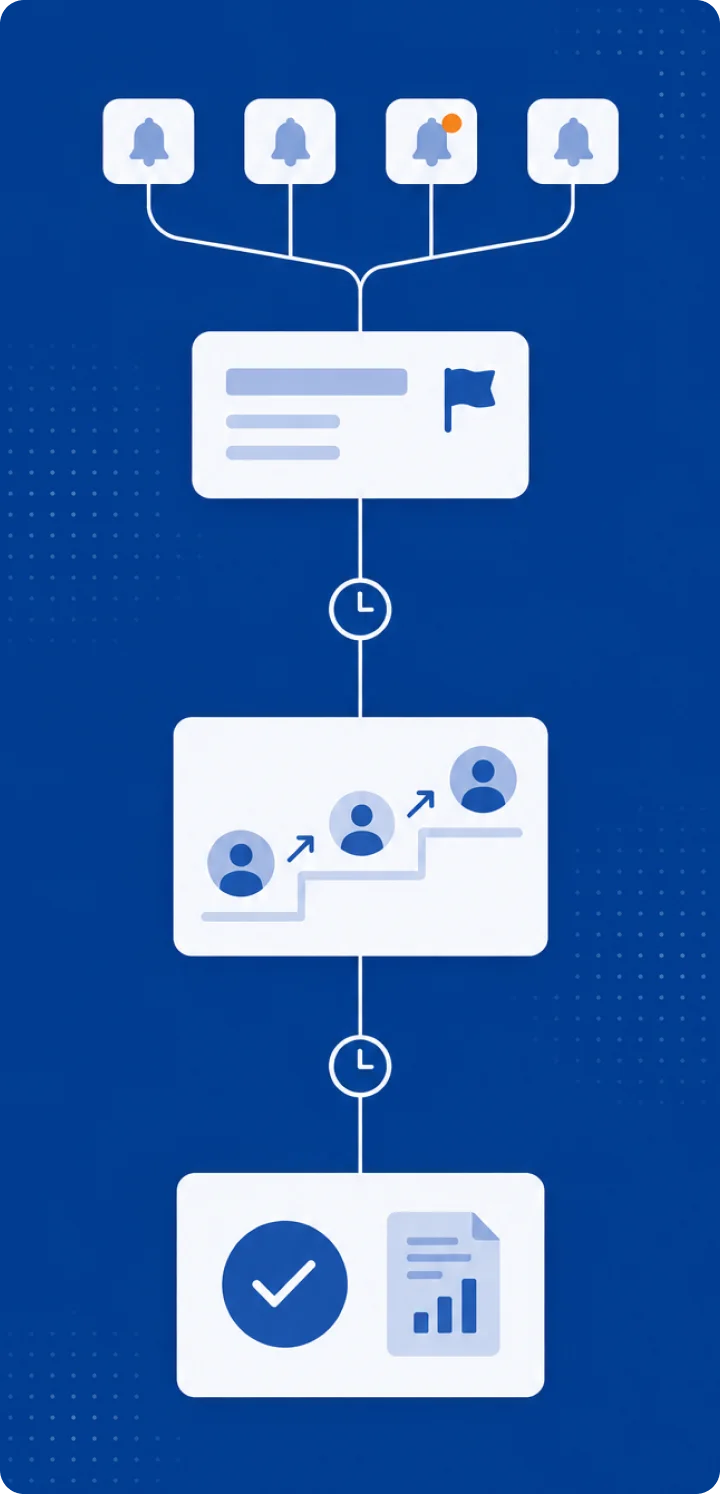
An analyst on shift acknowledges the alert, opens a ticket and runs the runbook remediation where one exists. For P1 and P2 incidents, the analyst pages the on-call senior engineer. You are notified when the ticket opens, within 15 minutes for a P1.
Do we need a new monitoring platform?
No. We ingest alerts from the monitoring tools you already run into our ticket queue. We report any coverage gaps found during onboarding, and any additional tooling is licensed in your name.
How does Holograph's NOC work with our IT team?
We work your alerts 24 hours a day and apply the remediation agreed in your runbooks. When L1 cannot resolve a ticket, it goes to an L2 engineer for deeper troubleshooting. When the fix is with your IT team or a vendor, we hand over the ticket with its full timeline. Your team confirms the resolution before it closes.
How is the monthly fee set?
You pay one monthly fee per customer. It covers monitoring, alert correlation, triage, escalation, ticketing, dashboard access and the monthly service review. One-off remediation, embedded engineers, hardware, tool licenses and add-on services are quoted separately.
How is the 15-minute P1 response measured?
A response means an analyst has acknowledged the alert and opened a ticket. Both steps are time-stamped, and the monthly service review reports the response time for every P1 against the target.
What is the difference between a NOC and a SOC?
A network operations center (NOC) monitors availability and performance: servers, networks, applications and databases. A security operations center (SOC) monitors for hostile activity: threat alerts, security events and log anomalies. Our core service is NOC monitoring, and SOC monitoring runs on the same desk as the Security operations add-on.
Can tickets go into our own ITSM tool?
Yes. Alerts can arrive in our shared NOC mailbox or in your own ITSM portal, and you can track every ticket on your dashboard.
What does the free coverage gap review include?
We document what you monitor today, which alerts arrive somewhere nobody reads, and where the gaps sit between your tooling and your working hours. You get the findings in writing and keep them whether or not you work with us.
Holograph pattern

Start With a Free Coverage Gap Review

Tell us which tools raise your alerts today, which hours your team covers and how many people are on it.