Trusted by 170+ Enterprise Clients

Your OpenAI Partner for Licenses, Use Cases and Team Training

Holograph is an OpenAI partner, with OpenAI-certified specialists on our team. We help you use ChatGPT Enterprise where it pays off and measures what each use case returns. The goal is more output from the people you already have.

Use Cases Picked on Return

Before anything is built, we score each AI idea on the data behind it and the return it can show. Only the ideas that hold up go ahead.

Company Data Stays in Your Workspace

We license ChatGPT Enterprise and set it up for your organization, so prompts and files stay in a workspace your admins control.

Every Team Trained on Its Own Tasks

We run hands-on training for each team that adopts a use case, built around the work that team does every week.

Token Spend Under Control

Our AI FinOps service shows token use by team and routes each task to the least expensive model that does it well.

Three Questions AI Makes Hard to Answer

Once AI tools are in daily use, the questions finance, auditors and on-call engineers ask get harder to answer. These are the situations that bring them up.
how it works

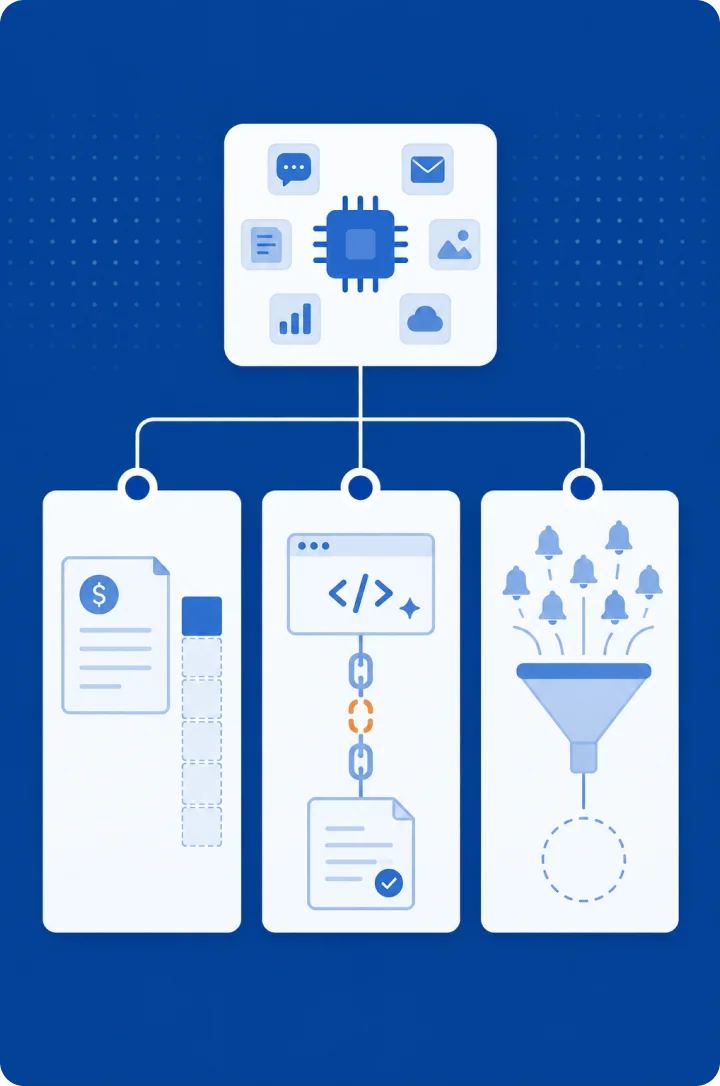
An AI Bill Nobody Can Break Down

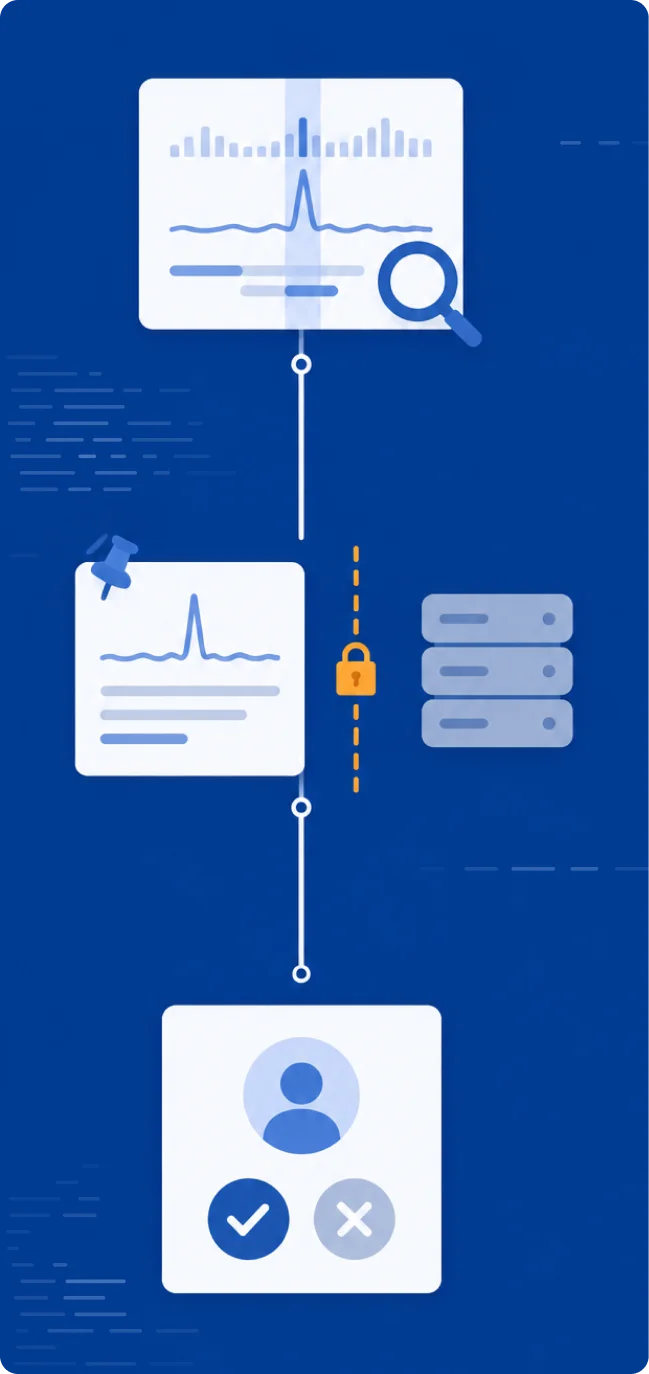
Your OpenAI or Amazon Bedrock invoice rose this quarter, and finance wants to know which team, model or product drove it. Copilot and ChatGPT seats renew separately, and unapproved tools sit on expense claims.

An Auditor Asks About AI-Written Code

The auditor wants to know which changes in the last release were AI-written, which requirement each one met and who reviewed it. Your pull requests hold none of that.

An Incident With Dozens of Alerts and No Clear Cause

One failure set off alerts across several monitoring tools, and the on-call engineer spent the first hour finding the one that mattered. The post-incident review was written from memory a week later.

What a Successful AI Pilot Leaves Open

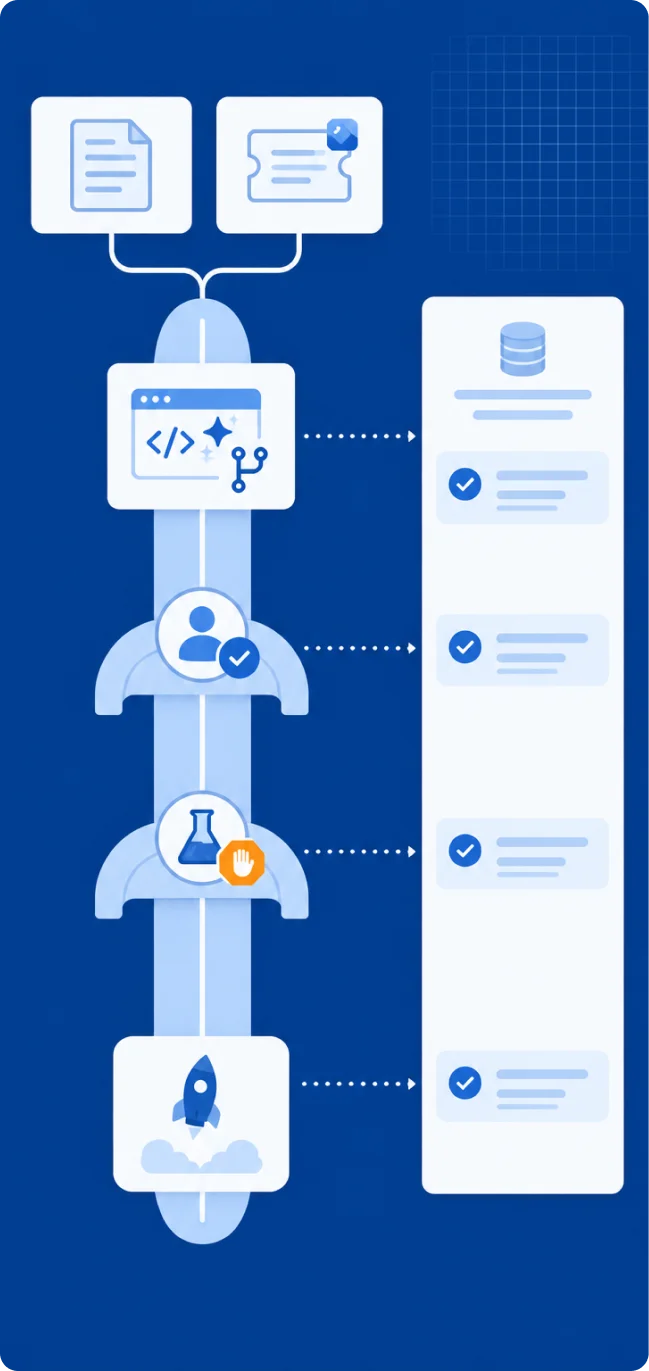
A pilot shows that a model or assistant can do the job. Three decisions are still open when it ends: who pays for it at scale, which systems it may touch and what record it leaves.

Governance work has no clear owner and shows nothing in a sprint review. It also competes for budget with the next use case, so it gets pushed back.
Holograph Pattern

Three Service Lines, One Entry Point

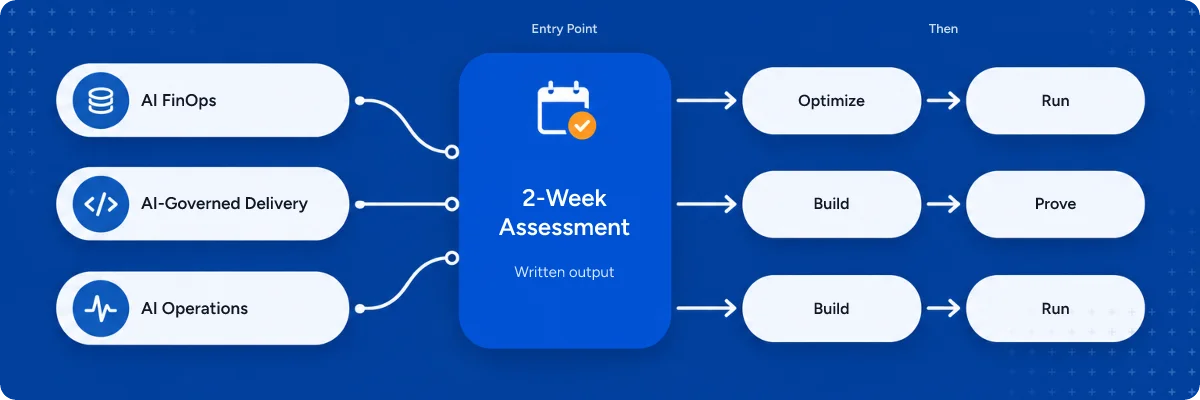
Each line starts with a two-week assessment with a fixed scope and ends in a written report that stays with you. You decide what comes next based on that report. The work is for CIOs, CTOs and finance leaders, and for the engineering and operations teams that run AI day to day.
Service line What it covers Assessment Written output
AI FinOps Spend on AI APIs, GPUs and seats AI Spend Assessment A one-page cost picture for finance and a ranked savings backlog
AI-Governed Delivery AI coding assistants and agents in your SDLC AI Delivery Readiness Assessment A gap report and a prioritized roadmap
AI Operations AI-assisted incident analysis AIOps Readiness Assessment A readiness report and prioritized use cases

Services

Control AI Spend Across APIs, GPUs, Seats and Shadow AI

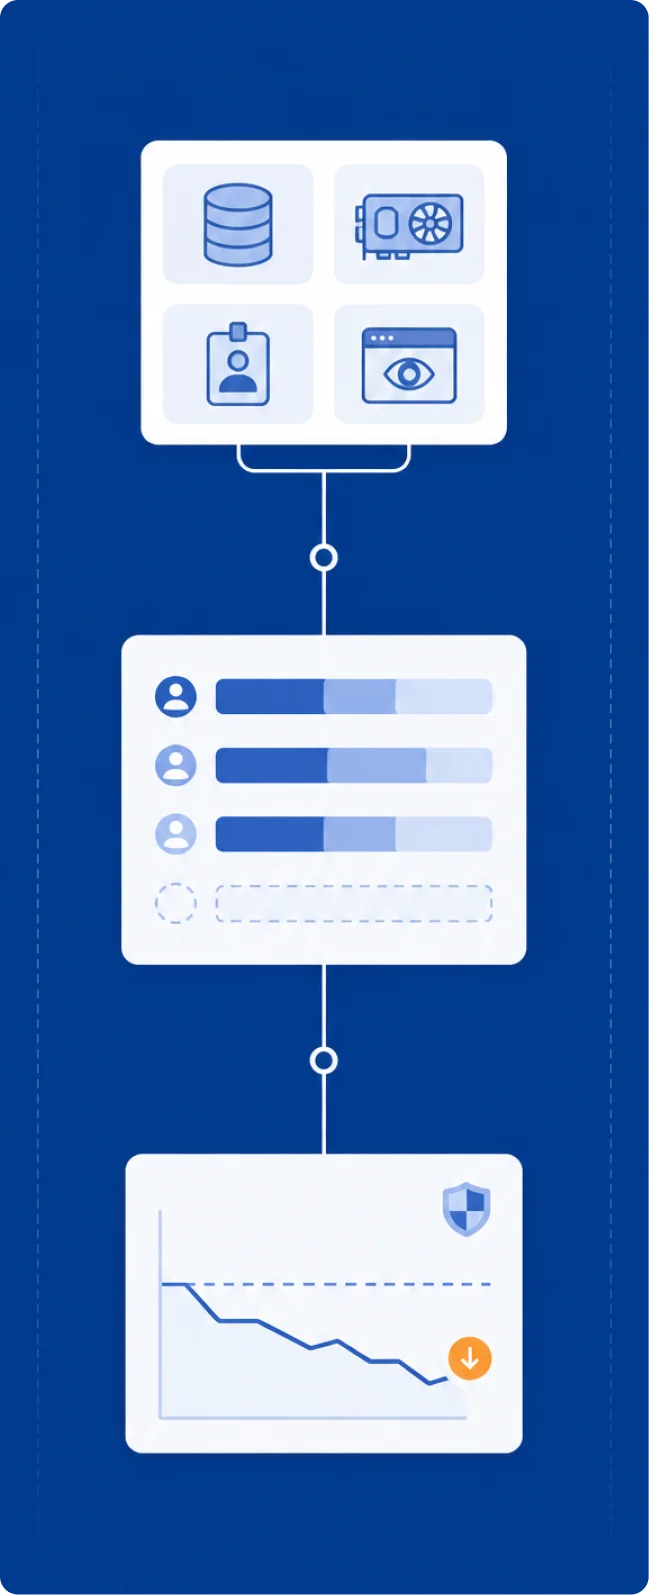
We inventory what you spend on AI, find what is paid for and unused, and put controls in place before the next renewal.
AI Spend Assessment
Assess
2 weeks | We inventory token usage, GPU hours, seats and API keys across your providers, and baseline the cost by team and use case. Output: a one-page cost picture for finance and a ranked savings backlog.
Vulnerability Assessment
Assess
We run authenticated and unauthenticated scans across your networks, servers and applications, remove false positives and prioritize results by risk.
Vulnerability Assessment
Assess
We run authenticated and unauthenticated scans across your networks, servers and applications, remove false positives and prioritize results by risk.
Vulnerability Assessment
Assess
We run authenticated and unauthenticated scans across your networks, servers and applications, remove false positives and prioritize results by risk.
Vulnerability Assessment
Assess
We run authenticated and unauthenticated scans across your networks, servers and applications, remove false positives and prioritize results by risk.
Vulnerability Assessment
Assess
We run authenticated and unauthenticated scans across your networks, servers and applications, remove false positives and prioritize results by risk.
Vulnerability Assessment
Assess
We run authenticated and unauthenticated scans across your networks, servers and applications, remove false positives and prioritize results by risk.

Harden the Network Edge and Every Endpoint

We inventory what you spend on AI, find what is paid for and unused, and put controls in place before the next renewal.
Vulnerability Assessment
Assess
We run authenticated and unauthenticated scans across your networks, servers and applications, remove false positives and prioritize results by risk.
Vulnerability Assessment
Assess
We run authenticated and unauthenticated scans across your networks, servers and applications, remove false positives and prioritize results by risk.
Vulnerability Assessment
Assess
We run authenticated and unauthenticated scans across your networks, servers and applications, remove false positives and prioritize results by risk.
Vulnerability Assessment
Assess
We run authenticated and unauthenticated scans across your networks, servers and applications, remove false positives and prioritize results by risk.
Vulnerability Assessment
Assess
We run authenticated and unauthenticated scans across your networks, servers and applications, remove false positives and prioritize results by risk.
Vulnerability Assessment
Assess
We run authenticated and unauthenticated scans across your networks, servers and applications, remove false positives and prioritize results by risk.
Vulnerability Assessment
Assess
We run authenticated and unauthenticated scans across your networks, servers and applications, remove false positives and prioritize results by risk.

Read-Only AI for Incident Analysis

We inventory what you spend on AI, find what is paid for and unused, and put controls in place before the next renewal.
Vulnerability Assessment
Assess
We run authenticated and unauthenticated scans across your networks, servers and applications, remove false positives and prioritize results by risk.
Vulnerability Assessment
Assess
We run authenticated and unauthenticated scans across your networks, servers and applications, remove false positives and prioritize results by risk.
Vulnerability Assessment
Assess
We run authenticated and unauthenticated scans across your networks, servers and applications, remove false positives and prioritize results by risk.
Vulnerability Assessment
Assess
We run authenticated and unauthenticated scans across your networks, servers and applications, remove false positives and prioritize results by risk.
Vulnerability Assessment
Assess
We run authenticated and unauthenticated scans across your networks, servers and applications, remove false positives and prioritize results by risk.
Vulnerability Assessment
Assess
We run authenticated and unauthenticated scans across your networks, servers and applications, remove false positives and prioritize results by risk.
Vulnerability Assessment
Assess
We run authenticated and unauthenticated scans across your networks, servers and applications, remove false positives and prioritize results by risk.

Pilot Scope and Measurement

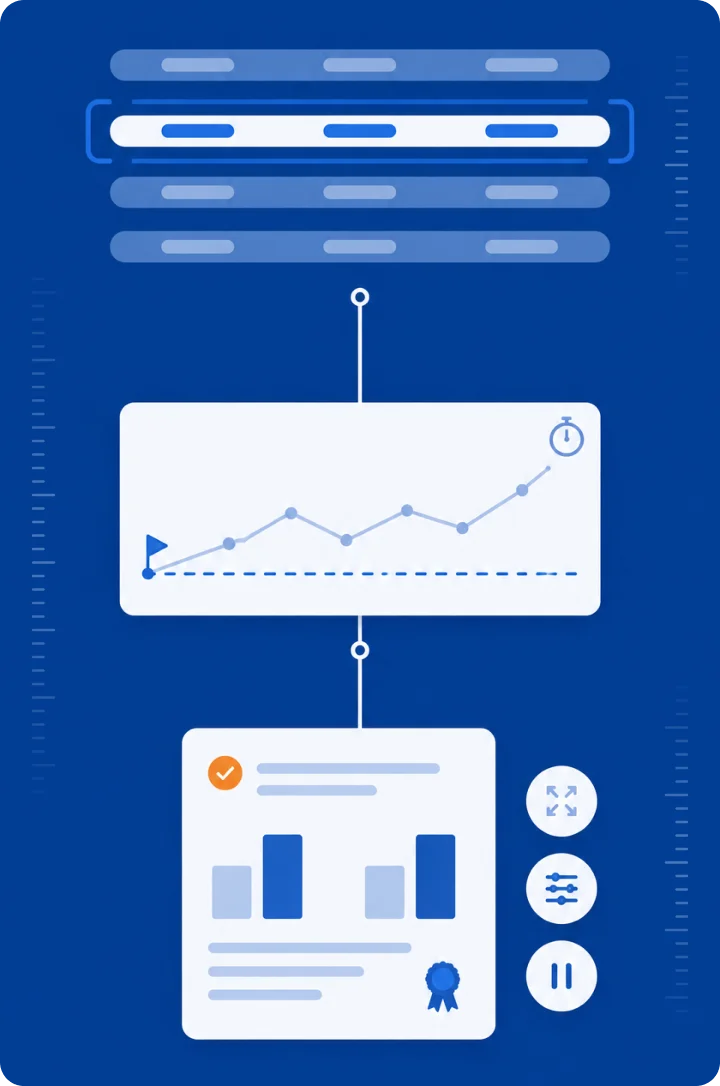
After the assessment, we run a pilot on your own systems. Before it starts, we agree on the scope, the measures and what counts as a result.
how it works
01

Scope

We agree in writing the targets, exclusions, testing windows, test accounts and rules of engagement.
02

Test

Testers work only inside that scope. We escalate critical findings as soon as we confirm them.
03

Report

We deliver evidence, reproduction steps, a risk rating and remediation guidance for each finding.

Your OpenAI Partner for Licenses, Use Cases and Team Training

Holograph is an OpenAI partner, with OpenAI-certified specialists on our team. We help you use ChatGPT Enterprise where it pays off and measures what each use case returns. The goal is more output from the people you already have.

Use Cases Picked on Return

Before anything is built, we score each AI idea on the data behind it and the return it can show. Only the ideas that hold up go ahead.

Company Data Stays in Your Workspace

We license ChatGPT Enterprise and set it up for your organization, so prompts and files stay in a workspace your admins control.

Every Team Trained on Its Own Tasks

We run hands-on training for each team that adopts a use case, built around the work that team does every week.

Token Spend Under Control

Our AI FinOps service shows token use by team and routes each task to the least expensive model that does it well.

Frequently Asked Questions

How is a penetration test different from a vulnerability scan?
A vulnerability scan identifies known weaknesses and misconfigurations at scale. A penetration test confirms which ones are exploitable, chains them into attack paths and finds logic flaws a scanner cannot see. A full assessment uses both.
Is VAPT the same as a penetration test?
VAPT combines a vulnerability assessment, which gives breadth across your assets, with a penetration test, which gives depth on the systems that matter most. We scope them together or separately, depending on what your auditor or customer asks for.
How is a test scoped?
We agree on the targets, IP ranges, applications and APIs in scope, the explicit exclusions, the user roles to test and the testing windows. We also agree rules of engagement and emergency contacts in writing before testing starts.
What happens if you find something critical during testing?
We pause testing and notify your named contact immediately. Testing resumes once containment is agreed.
What access do you need from us?
External tests need no access. Internal tests need a network foothold, such as a VPN account or a test laptop on your network. Application tests need a test account for each role in scope, and configuration audits need read-only access.
What access do you need from us?
External tests need no access. Internal tests need a network foothold, such as a VPN account or a test laptop on your network. Application tests need a test account for each role in scope, and configuration audits need read-only access.
Can you help us answer a customer security questionnaire or an insurance renewal?
Yes. We map each question to the relevant controls, assess them, and provide supporting evidence such as test reports and access review records.
Do you work to ISO 27001 or SOC 2?
We help organizations prepare for ISO 27001 certification and SOC 2 audits, starting with a gap assessment. We are not certified against either standard ourselves.
Who carries out the work?
Certified practitioners holding CEH, OSCP, CHFI and CREST certifications carry out the work under our contract and NDA. A dedicated Holograph project manager owns the engagement from purchase order to handover.
Is retesting included after we fix the findings?
Retesting is agreed case by case, most often when reported findings are challenged and need to be verified again.
How long does an engagement take, and when is the report delivered?
Timelines depend on scope, including the number of applications, networks and user roles being tested. We agree on the testing window and the report delivery date in writing during scoping, before work starts.
Holograph pattern

Start With a Two-Week Assessment

Tell us what you need tested, hardened or monitored, the environment
involved and the deadline you are working to.